Meter Historian Test Copies: Close and Dispose of Recovery Data
Meter historian test copy disposal should close the isolated recovery environment, identify every temporary copy, confirm retention obligations and use an approved method appropriate to the storage system. Do not delete the production archive or the protected backup used to create the test. Keep enough completion evidence to show what was closed, who authorized it and what remains under retention. A successful restore is only part of the exercise: temporary databases, exported files, snapshots, credentials and third-party working copies can outlive the test unless someone is responsible for closing them.
Define what the recovery exercise created
Start with an inventory of the isolated test environment. Record the restored database or archive, host or service, snapshot references, extracted files and approved users. Include working copies made for comparison and any files sent to a support provider. A test label alone does not establish that the environment is isolated or that all its contents can be discarded.
Distinguish three categories: production records, protected recovery sources and temporary exercise outputs. The first two may need to remain available even after the exercise ends. The third category needs a documented retention decision. If the exercise revealed a fault, some outputs may become evidence for an open investigation and need controlled retention rather than immediate removal.
Use the existing meter historian restore acceptance guide to establish whether the restored information was actually checked. This article addresses closure after testing; it does not replace the technical restore or acceptance process.
Confirm authority and retention before removal
Ask the data owner to confirm the exercise is complete and that no investigation, contract or other retention obligation requires the temporary material. Document the decision rather than treating a quiet support ticket as permission. If ownership is uncertain, restrict access and resolve the ownership question before destructive action.
The NIST media sanitization publication provides authoritative background for selecting sanitization practices. It does not make ordinary file deletion equivalent to media sanitization. The applicable method depends on the storage technology, sensitivity and intended disposition, and should follow an approved organizational process.
The checklist below is a suggested exercise closure record, not a legal retention schedule or a claim that the meter itself contains a historian. Replace its generic roles with named owners and actual storage references in the site’s controlled record.
| Closure item | Required decision or evidence | Reason to leave it open |
|---|---|---|
| Exercise result | Accepted result or documented outstanding defects | Restore verification is unfinished |
| Data scope | Explicit separation of test outputs and protected sources | Production and test references are ambiguous |
| Retention | Owner approval and any evidence hold | Investigation or contractual need remains |
| Copy inventory | Databases, exports, snapshots and support copies | Additional copies have not been located |
| Access | Accounts, tokens and permissions used by the exercise | Temporary access still reaches retained data |
| Disposition | Approved method and execution evidence | Storage platform cannot support the proposed method |
| Verification | Independent review of the actual completion state | Only an unverified deletion request exists |
Close activity before closing storage
Stop scheduled tasks that can recreate exercise outputs. Check test data collectors, report jobs, synchronization services and export scripts. A directory may be empty immediately after deletion but populated again by an unattended job the next morning. Confirm which tasks belong to the test and avoid disabling production collection by association.
Disconnect test integrations using the platform’s approved process. Verify that dashboards and automated reports are not still reading the temporary environment. If a report has become dependent on the exercise database, resolve that dependency before closure. The purpose is to remove the temporary environment without accidentally removing a service that others have started using.
The restore dependency register guide can help identify services, credentials and reference files used during the recovery. Use that register as an input, then record actual closure results. A dependency list prepared before testing may not include every export produced during troubleshooting.
Match the disposition method to the storage boundary
A local file, a database table, a virtual-machine snapshot and a managed cloud backup are different objects. A command that removes one does not establish the state of the others. Ask the storage owner which replicas, retained versions and recovery mechanisms apply to the particular system.
Do not run an improvised whole-drive wipe on a shared production host to remove a temporary export. That could destroy unrelated records and services. Use a documented approach appropriate to the approved scope. Where underlying storage is shared or managed by a provider, rely on the platform’s documented controls and obtain the completion evidence the site’s process requires.
Encryption also needs a defined boundary. Removing one user’s access does not prove that every copy or encryption key has been removed. Cryptographic erasure, when selected by an approved process, has prerequisites that must be established for the actual system. Avoid treating a familiar security term as a substitute for checking storage behavior.
Account for snapshots, exports and support copies
Ask the exercise team where data moved, not only where the original restore was placed. Temporary spreadsheets, downloaded reports and diagnostic bundles can be outside the main test host. Record the person or service responsible for each copy and the disposition state. A supplier’s acknowledgement may be part of that evidence when a supplier held a permitted working copy.
Some backups expire under a managed retention policy rather than disappearing immediately. Record that limitation accurately, including the owner and expected review date. Do not report that all data is erased while retained snapshots still contain it. Restrict access and prevent inappropriate reuse during the remaining retention period.
For records that must be kept, transfer them into an approved retained-evidence location and give them a clear purpose. Keeping an entire abandoned test server because one screenshot is needed usually leaves unnecessary exposure and operational ambiguity. Retain the required evidence at the smallest appropriate scope, subject to the owner’s policy.
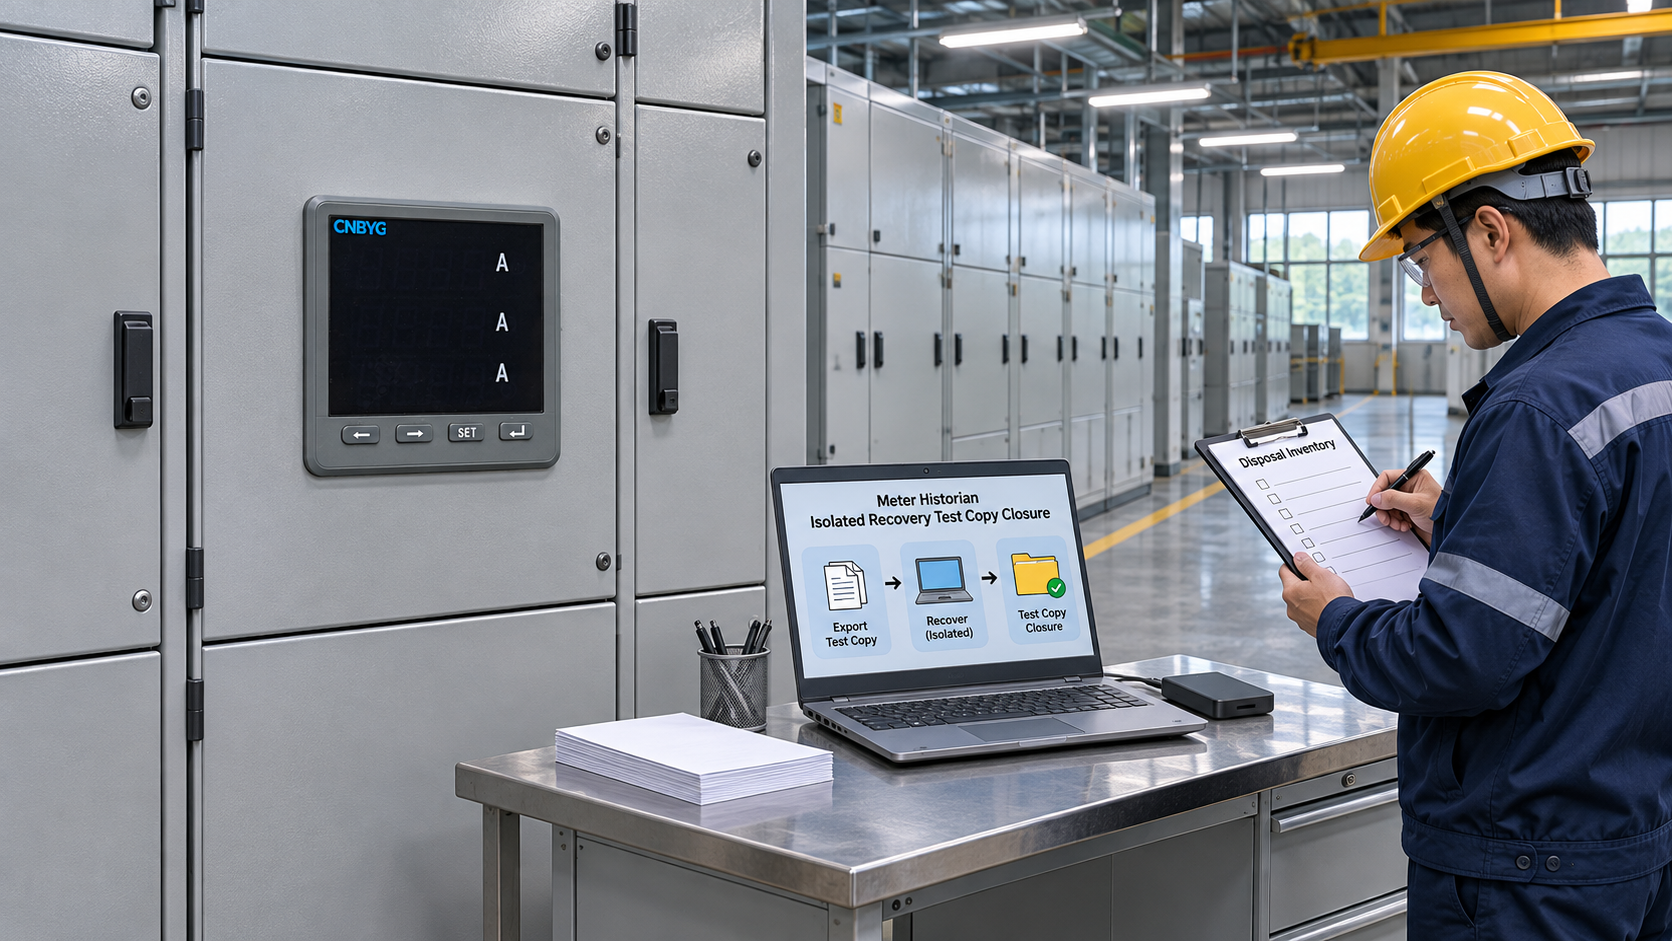
Worked example: closing an isolated monthly archive test
Consider a hypothetical factory recovery exercise involving an external monitoring archive. The team restores a protected backup to an isolated test service, runs sample comparisons and exports a short validation report. This example does not describe a CNBYG customer installation or a function built into a BY194 instrument.
At closure, the owner identifies the test service, its snapshot, two comparison exports and one support copy. The protected backup remains under its normal retention policy. The signed validation report is transferred to the exercise record. The temporary objects receive disposition decisions individually, with an owner and verification result for each.
One snapshot remains under an enforced retention setting. The team records it as retained pending expiry, restricts access and schedules a check. The report therefore says that active test services and ordinary working copies are closed while a named snapshot remains under controlled retention. This is a more useful result than an unsupported statement that everything has been erased.
Verify the result without creating another uncontrolled copy
Read back the platform’s current state after the authorized action. Confirm that the targeted service or object no longer appears in its active inventory, scheduled jobs are closed and temporary accounts cannot be used. Record the verification method and reviewer. A successful request response alone may not mean a long-running storage operation has finished.
Avoid downloading another full archive solely to prove that a copy existed. Prefer the relevant object identifiers, completion records and minimally necessary screenshots. Keep the closure evidence in its approved location. If verification reveals an unexpected retained copy, reopen that item and investigate rather than silently excluding it from the count.
The OWASP logging guidance provides background on protecting records and considering copies during retention and disposal. This workflow applies those general ideas to an external meter-data recovery exercise; its particular checklist is an engineering recommendation rather than a quoted standard.
Keep product responsibilities separate from archive responsibilities
The BY194 series product page identifies the relevant instrument family. Confirm the exact device documentation and ordered options when planning an integration. Do not infer internal storage, secure erase or recovery features from the instrument’s front appearance.
In many installations the historian, backup service and supplier portal have separate owners. Include those owners in the closure plan. The meter supplier can answer questions within its documented product scope, while the platform owner controls archive retention and storage operations. The meter decommissioning data handover guide covers the different situation in which an actual device or service is being retired.
The following educational video explains why deleting a file and removing recoverable information are different questions. It is background material, not an approved procedure for a particular drive, cloud service or industrial system.
Frequently asked questions
Does deleting the test database remove its snapshots?
Not necessarily. Snapshots, replicas, exports and backups can have separate lifecycles. Confirm the actual platform behavior and record each remaining object with its owner and retention or disposition decision.
Should the protected recovery backup be deleted after a successful test?
No automatic deletion follows from a successful test. The protected source remains subject to its own retention and recovery requirements. The exercise closure should distinguish it explicitly from temporary outputs.
Can access revocation replace data disposal?
Access restriction can be an interim or complementary control, but it does not establish that stored copies have been removed or sanitized. Record access state and storage disposition as separate results.
What if a retained snapshot cannot expire immediately?
Document the retained object, restrict access, identify the responsible owner and set a follow-up check under the applicable retention policy. Report that limited state accurately instead of claiming complete erasure.